Article sectionsMove directly to a section, or continue reading normally.
Why security matters—even for small projects
Breaches don’t ask for your project size. A small API mistake can expose data or permissions.
Non-negotiable essentials
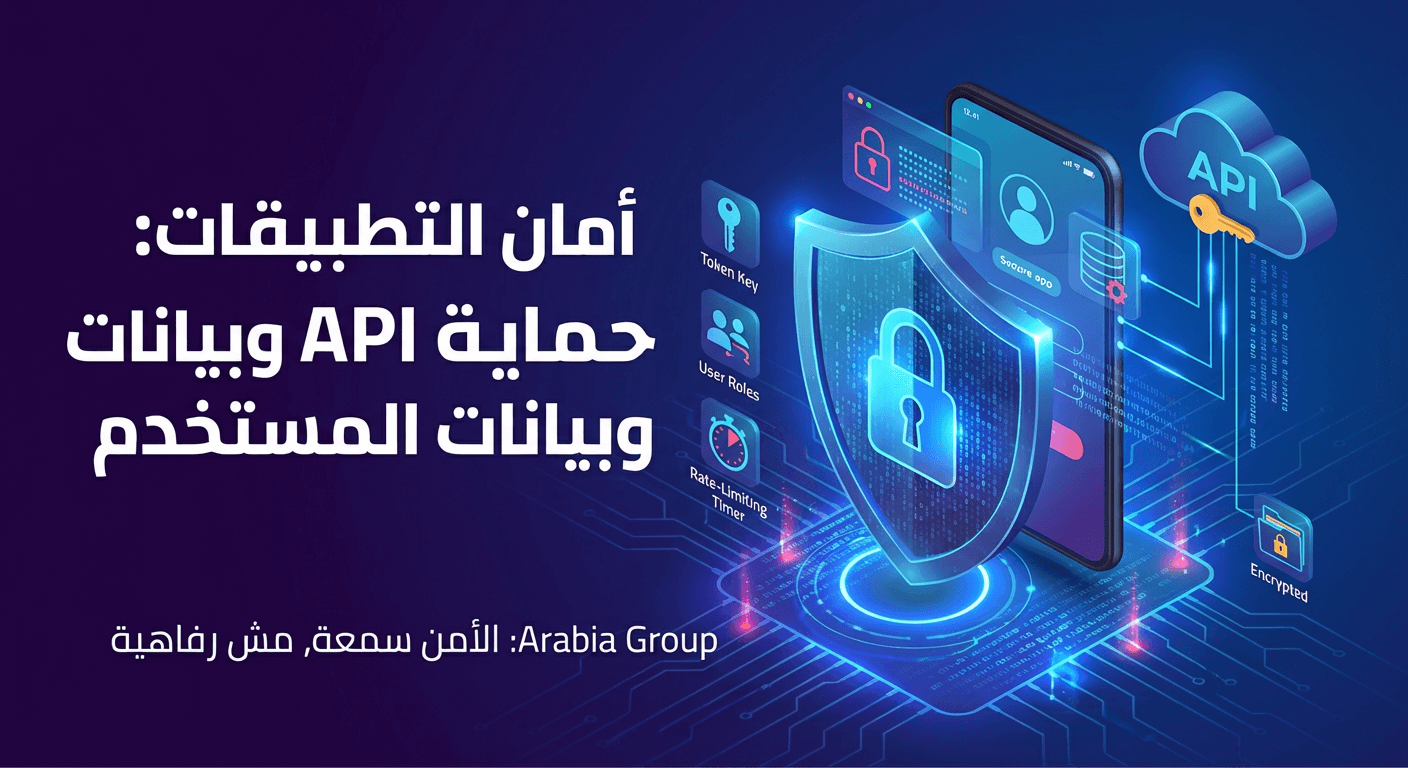
- Strong authentication: tokens with expiry (Sanctum/JWT).
- Roles & permissions: never keep everything open.
- Rate limiting: blocks abuse and protects servers.
- Server-side validation: never trust the client.
- Encrypt sensitive data: especially personal information.
Common mistakes
- Verbose errors that reveal infrastructure details.
- Same permissions for every user.
- No audit logs for sensitive actions.
Arabia Group’s approach
Arabia Group ships APIs with disciplined security: permissions, rate limits, strict validation, and proper production configurations. Security isn’t luxury—it’s reputation.